

Author: Toon Segers, Director National Security, Roseman Labs
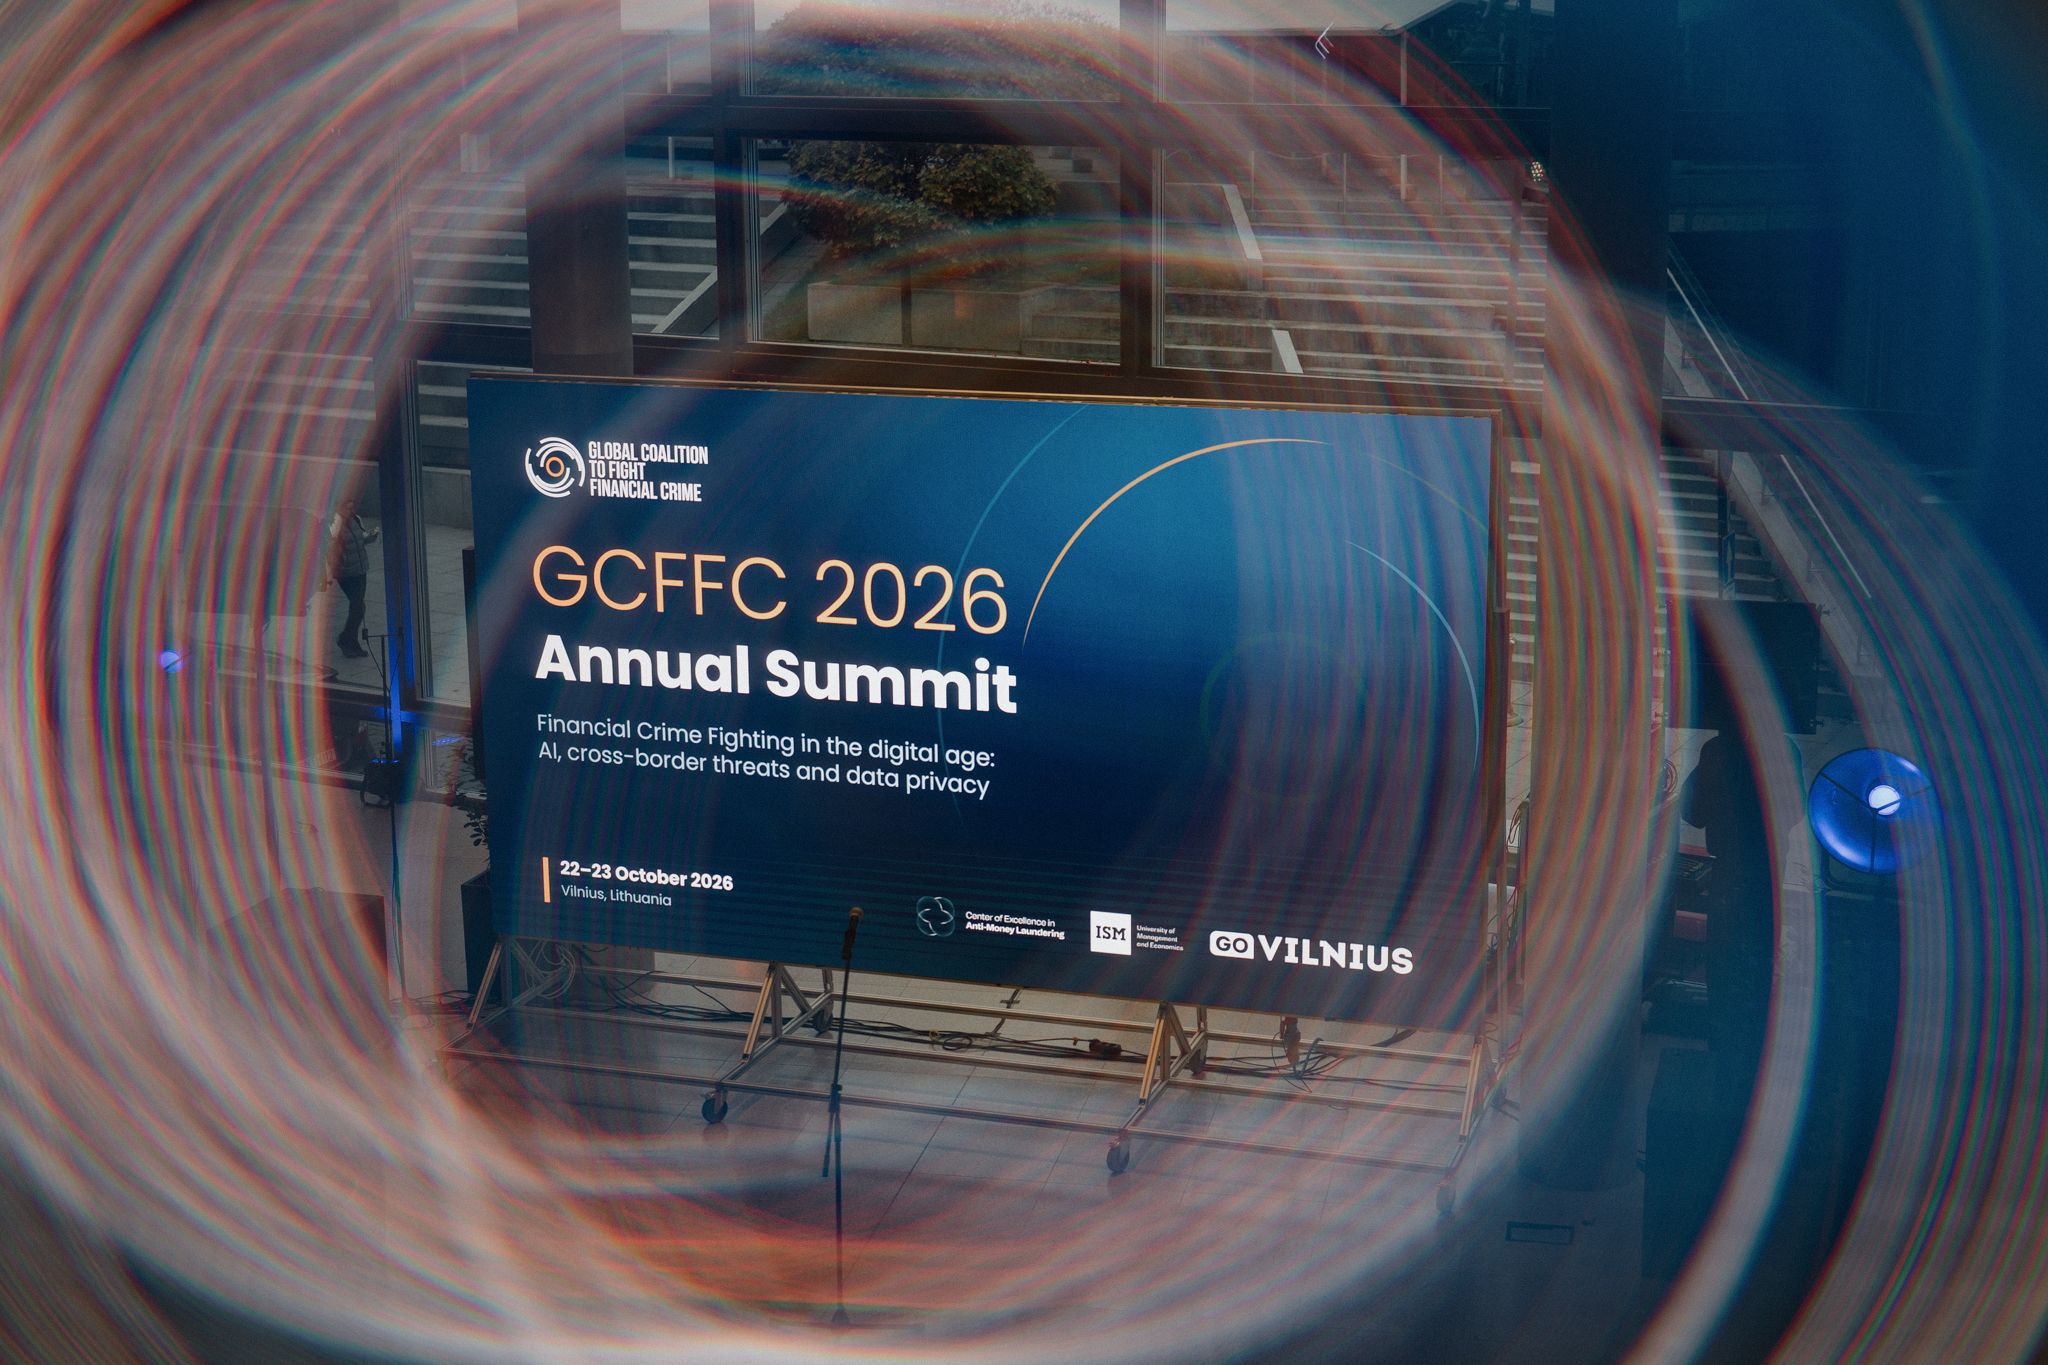
At the Global Coalition to Fight Financial Crime Annual Summit 2026 in Vilnius, I joined the panel Finding the balance between GDPR and Financial Crime Prevention in Europe.
The focus was that banks increasingly accept that they need to share intelligence, and the next step is how to do it under safeguards that regulators can trust.
The discussion was moderated by Vivienne Artz OBE, an authority at the intersection of privacy and financial crime. I was honoured to sit aside Alessandra Pierucci from the European Data Protection Board (EDPB), Tobias Thygesen from the EU Anti-Money Laundering Authority (AMLA), and Felix Goodenough from Data Technology for Compliance.
What I found especially valuable was the regulatory cooperation reflected in the composition of our panel. Rather than discussing AML effectiveness and data protection in separate rooms, representatives of both authorities were part of the same conversation with industry practitioners. This allowed us to connect the emerging regulatory framework directly to the practical experience of building information-sharing partnerships.
Joint guidelines under Article 75
AMLA and the EDPB are jointly drafting guidelines on information-sharing partnerships under Article 75 of the EU Anti-Money Laundering Regulation. Tobias and Alessandra lead that work from the AML supervision and data protection perspectives respectively.
The joint approach reflects the nature of these partnerships. Article 75 is intended to enable cooperation against financial crime, but these partnerships necessarily involve the processing of personal data. The joint guidelines therefore aim to provide practical clarity on how effective information sharing and the protection of personal data can go hand in hand.
Article 75 applies from 10 July 2027 for most obliged entities, and a public consultation on the draft guidelines is planned for the first half of 2027. Under Article 75(2), institutions must notify their supervisor before a partnership begins, and supervisory verification must be completed first. A partnership therefore has to demonstrate in advance how it will protect personal data.
Moving beyond “privacy versus effectiveness”
Previously, discussions about financial-crime information sharing have been framed as a trade-off: institutions could either share more information and improve detection, or protect privacy by limiting collaboration.
The discussion in Vilnius pointed towards a constructive approach: the objective is not to choose between privacy and effective financial-crime prevention. It is to design partnerships in which both objectives can be achieved together. As Vivienne Artz reflected after the panel, active cooperation between the two regulators should improve certainty and confidence around effective data sharing, while also opening the door to new technologies as practical enablers.
In the second half of the panel, drawing on our work in Germany and elsewhere, I set out where Privacy Enhancing Technologies (PETs) fit. PETs reduce the privacy and security risks within the processing itself, and should not be seen as waiving or relaxing obligations. Proportionality and accountability apply in full, and are enforced by PETs through data minimisation, purpose binding, and effective verification by supervisors.
Learning from operational practice in Germany
The discussion turned to practical examples, including the fraud information-sharing network initiated by Commerzbank, Deutsche Bank and DSGV - supported by Roseman Labs, and our partner spotixx. The significance of this initiative is not simply that banks are collaborating. It is that privacy safeguards such as data minimisation and purpose binding can be built into the technical architecture of the collaboration. Institutions jointly identify relevant signals without creating a central pool of their underlying customer and transaction data.
Our experience is that privacy technology can create a positive-sum outcome. By operating as a network, banks can improve their ability to detect fraud and financial crime. At the same time, PETs can reduce unnecessary exposure of personal data, limit processing to agreed purposes and produce verifiable records of how the collaboration operates. This matters not only to participating banks, but also to the regulators assessing the partnership. Clear controls, verifiable governance mechanisms built into the solution, and defined outputs can make the residual risks easier to understand and the safeguards easier to verify.
The ambition for 2030
Looking towards 2030, there was broad recognition that banks will increasingly need to operate in networks because criminals already do. Fraud and money laundering rarely remain within one institution. An account may be opened at one bank, a victim’s credentials compromised elsewhere, and the proceeds transferred through several other institutions and jurisdictions. Each organisation sees one part of the sequence. The network can see more of the pattern.
The ambition should therefore be an open and interoperable ecosystem in which institutions can collaborate on fraud, money laundering, sanctions evasion and related threats, with strong data minimisation, purpose binding and governance built in from the beginning. This does not mean sharing all available data. Quite the opposite. The objective should be to generate better intelligence with less exposure.
From whether to how
What stood out to me at the GCFFC Summit was the energy now concentrating around secure information-sharing partnerships. There is increasingly broad recognition that financial institutions must be able to work in networks if they are to address networked crime effectively. Attention is shifting beyond the necessity of collaboration, towards how those partnerships should be governed, supervised and implemented.
PETs are one important route, but they sit within a wider framework of legal certainty, robust governance, clear purposes and institutional accountability. Technology does not replace those requirements. It can, however, make important safeguards more concrete, enforceable and verifiable.
Regulators are also inviting practitioners to contribute good practices and operational experience to the development of the guidelines. The initiatives emerging in Germany, the Baltics and elsewhere can provide valuable evidence of what works, where the remaining barriers lie and how privacy protections can be embedded into collaboration by design.
For Roseman Labs, the panel was an encouraging sign of progress. The financial-crime and data-protection perspectives are not being developed in isolation. They are being brought together, and industry is being invited into the conversation to help translate regulatory objectives into workable models. The opportunity for Europe is to replace the old choice between privacy and effectiveness with a better question:
How can institutions share what their data knows, while revealing as little of the underlying data as possible? That is the basis on which trusted information-sharing partnerships can scale.
Generate new insights on sensitive data with Roseman Labs’ secure Multi-Party Computation technology. Want to find out how your organization can do that? Contact us using the form below.